

Uh Oh! There Are More Victims of the Cyberattack On EY (But It Doesn’t Have to Happen to You)
So how did it happen?
UBX Cloud
Back in the spring, the Big Four accounting firm EY (that stands for Ernst & Young) was the target of a major data breach. This was publicly disclosed in July.
What wasn’t made public until just this past week was some of the EY clients whose data was exposed as a result of the attack.
We now know that clients of the Goldman Sachs wealth management division, as well as the UK-based hedge fund known as Man Group and global real estate developer Tishman Speyer, had their data exposed.
Clients of all three had both personal and financial information compromised, including (according to New York state officials investigating the attack) “name, address, tax identifier, email address, financial information.”
Don’t overlook the importance of that last one.
And that’s just what we know so far. It’s possible EY will come out later and say that more outside firms or individuals had their information exposed.
So how did it happen? Apparently it started with an attack on some vulnerable third-party software. A hacker group calling itself ShinyHunters has a dark web leak site (because of course it does), and they issued a statement saying they were the ones who got to EY.
ShinyHunters are a bunch of busy beavers, having taken down quite a few major companies since they started doing this in 2020 and, at least according to them, successfully hacking the FBI – from which they stole thousands of bureau personnel records.
One of the culprits at ShinyHunters was recently arrested by Dutch police and claims that the group has taken in $70 million in extortion payments.
Meanwhile, Goldman Sachs is not happy with EY, and is demanding EY “demonstrate their remediation efforts are effective through objective evidence and third-party validation.”
No one in this business can claim to be perfect, and the nature of cyberthreats is that they often evolve faster than the cybersecurity industry can keep up.
But if EY really got hacked through third-party software, that is a pretty blatant security failure.
Our technology stack has excellent tools to check for vulnerabilities in third-party software and address them before these programs ever have a chance to become active on your system. It happens automatically in real time, and our tools instantly secure any potential issues and inform both you and our 24/7 Security Operations Center team immediately.
So while it would be awfully brash to claim “it could never happen here,” we read a story like this and shake our heads. A company the size of EY could certainly afford the tech stack and team we have at UBX Cloud. Then again, so can any company. It’s ridiculously affordable if you access it through us.
Especially when you consider the cost of what EY and its major clients have been going through this year.
If you own a company that deals in sensitive client data – or any other sensitive data for that matter – here’s a chance to prove you’re smarter than EY. Give us a call at 586.322.5000 and let’s make sure we close off any vulnerabilities like the ones that got EY hacked.
It does not need to happen to you. Let’s get to work!
Related Posts
All posts

TV Station Ghosted by Cloud Storage Provider Endures Ordeal To Reclaim Data: Here’s Why It Won’t Happen If You Work With Us
The station (Nine PBS) was storing data with Open Source Storage (OSS).
Cybersecurity Stocks Soared This Week, Because ‘Lost In Space’ Was Right About Agentic AI
If you’ve invested in cybersecurity stocks, you’ve had a very good few days.
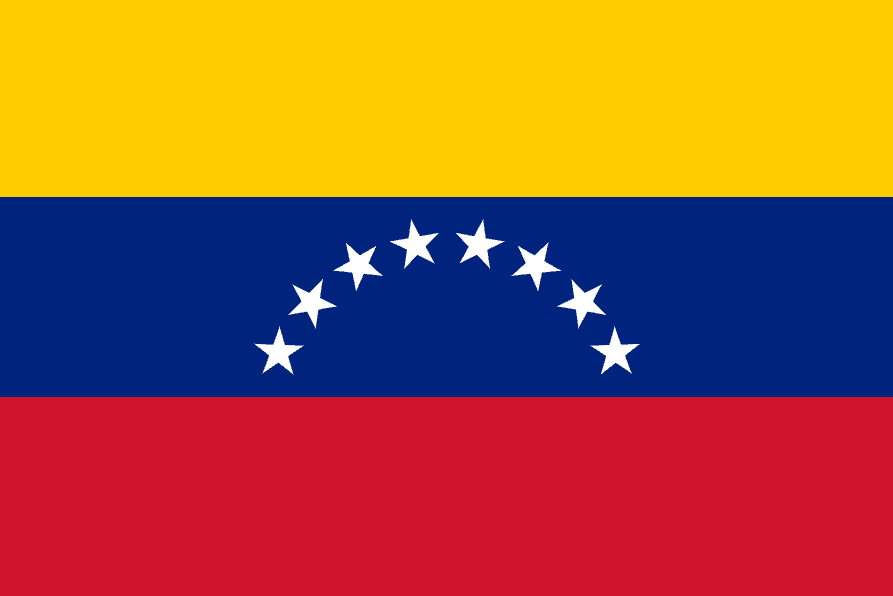
Respect to Our Valued Team Members in Venezuela
We want to take a moment to recognize the exceptional strength and courage of our team members in Caracas, Venezuela.